THREAT RESEARCH // ACTOR ATTRIBUTION & DE-ANONYMISATION
TeamLeets Unmasked: How an SMTP Relay Slip Exposed a Transnational Hacking Syndicate
From an intercepted test subject line to code repositories, PayPal endpoints, and tribal mourning rituals across Pakistan and Morocco.
Published: October 2026 | Reading Time: 18 min
1. Executive Summary
In threat intelligence investigations, high-volume malicious campaigns often leave subtle operational traces during their initial testing phase. What appeared to be routine scanning activity quickly escalated into an exhaustive de-anonymisation investigation following a single operational security (OPSEC) failure by an adversary testing an outbound SMTP relay.
Key Findings at a Glance:
- The Attribution Trigger: An outbound transmission test bearing the explicit custom identifier
"SMTPs DaGunnaPK1337"provided the cardinal pivot moniker for the entire investigation. - Syndicate Unmasking: Identification and infrastructure mapping of the cross-border cyber syndicate TeamLeets, operating across Pakistan, Morocco, and Iran.
- Natural Person Resolution:
- Muhammad Haris (operating as Harry_Haxor / Haris Qureshi): unmasked in Islamabad, Pakistan via unscrubbed Git commit headers, social media records, and keynote speaker appearances at national technology conferences.
- Hassan Arbaoui (operating as a2svs / Hamza Anonime): unmasked in the Rif region of Morocco via direct PayPal payment endpoints, public web-shell staging repositories, and virtual US VoIP telephony.
- Commercial Exploitation: Uncovering an underground commercial storefront operated on Telegram by syndicate administrator ChiefYoru, marketing exploit subscriptions and SMTP checking tools under the banner "TEAMLEETS (ULTIMATE) EDITION" for $50 USDT.
- The Sajjad Dahri Memorial Nexus: Multi-domain cross-correlation revealed the syndicate's unifying event: a coordinated 100+ domain mass-defacement campaign executed in May 2024 to memorialize their deceased associate Sajjad Dahri, validated through Sindhi tribal kinship structures and burner sockpuppet accounts.
- Responsible Disclosure & PII Masking: In accordance with intelligence standards and privacy compliance, sensitive identifiers (such as personal email addresses, phone digits, and direct profile IDs) have been partially redacted.
2. The Genesis: The "SMTPs DaGunnaPK1337" Relay Slip
The investigation commenced following the interception of outbound message telemetry originating from an unauthorized SMTP relay node. An adversary had established access across distributed network nodes and was validating relay delivery throughput prior to launching mass mailings.
During this validation phase, the operator committed a critical operational security blunder: rather than employing generic subject headers or randomized test strings, the attacker broadcast test messages containing their personal hacker handle.
[+] Intercepted Message Trace Record
├── Message Subject: "SMTPs DaGunnaPK1337"
├── Secondary Subjects: "Test Email", "SMTP Test Email"
├── Transmitting Origin IPs:
│   ├── 150.251.225.4
│   ├── 86.104.249.200
│   └── 135.136.11.37
└── Authentication Footprint: Distributed residential proxies (Casablanca, Rabat, Tehran)
This premature broadcast yielded the primary pivot artifact: DaGunnaPK1337.
A preliminary linguistic dissection of the moniker revealed three constituent components:
DaGunna: A stylized street and hip-hop cultural reference adopted by online threat actors.PK: The ISO 3166-1 alpha-2 country code for Pakistan.1337: Standard hacker leetspeak representing "Elite".
Pivoting from this distinctive handle across open-source repositories and messaging platforms revealed that DaGunnaPK1337 maintained an active channel on Telegram (t.me/DaGunnaPK1337). In his channel biography and broadcast feeds, the actor openly announced his nationality, targets, and prolific attack cadence. Rather than concealing his activities, the operator used the channel as an operational showcase, regularly boasting of his high-volume mass-defacement operations.
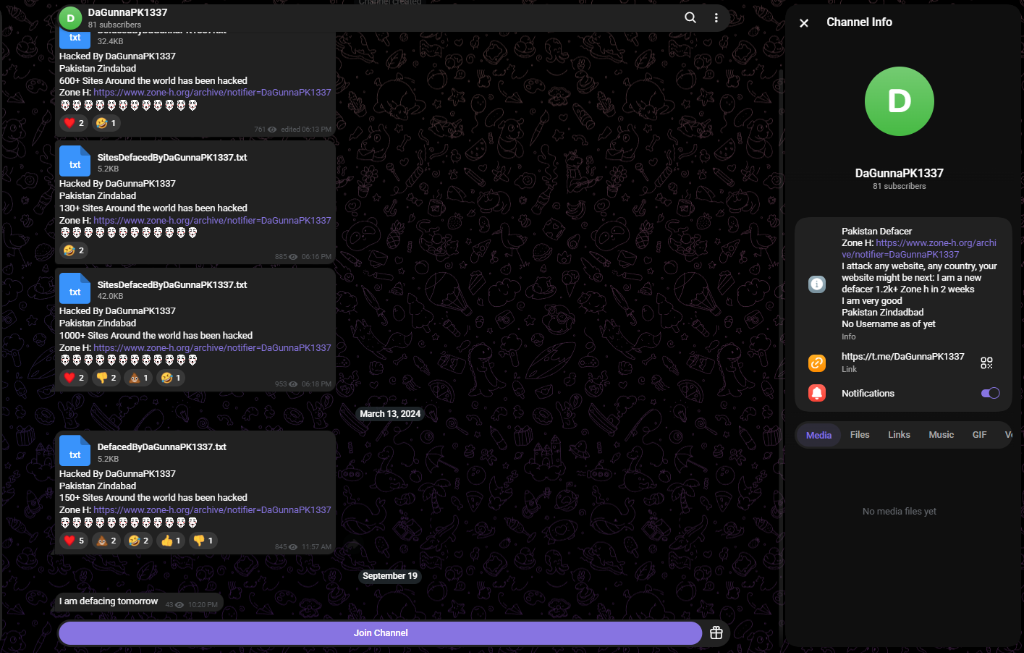
t.me/DaGunnaPK1337) displaying the actor's verified bio claiming over 1,200 Zone-H defacements in two weeks, alongside broadcast updates celebrating successive waves of 150, 600, and 1,000+ compromised websites.
The overt claims logged in this channel established that the actor was not an isolated hobbyist, but an aggressive exploit operator actively searching for vulnerable servers to compromise in bulk. Forensic examination of the broadcast timestamps demonstrated that his attack bursts closely aligned with the outbound relay telemetry intercepted on our monitored nodes.
Furthermore, the operator's public boasts provided key operational intelligence: his defacement targets were systematically registered on third-party mirror archives like Zone-H. By tracing these mirror submissions, investigators uncovered an interconnected network of co-conspirators who routinely shared exploit payloads, credential lists, and defacement credits.
3. Syndicate Architecture: Mapping the TeamLeets Network
To reconstruct the broader threat ecosystem surrounding DaGunnaPK1337, investigators conducted extensive entity resolution and link-analysis modeling using Maltego. Seed entities including observed IP addresses, email handles, cryptographic transaction IDs, and hacker aliases were mapped against public defacement archives, code hosting repositories, and social networks.
The resulting transform model synthesized 48 unique threat entities connected by 51 directional vectors. This graph demonstrated that DaGunnaPK1337 did not operate in isolation; rather, he functioned as a primary exploit operator within a structured, transnational cyber collective known as TeamLeets.
Link analysis revealed that TeamLeets operated with functional division of labor across three primary operational hubs:
- Pakistani Offensive Cell: Spearheaded by
DaGunnaPK1337andHarry_Haxor, responsible for active target scanning, automated CMS exploitation, relay hijacking, and mass defacements. - Moroccan Infrastructure Cell: Commanded by
a2svs(operating as Hamza Anonime), responsible for custom web-shell development, backdoor authoring, VoIP communications, and receiving illicit remittances. - Commercial & Distribution Arm: Administered from Tehran by
ChiefYoru, managing public Telegram channels and commercial exploit storefronts.
The operational roles and resolved real-world identities of the core syndicate members are summarized in the matrix below:
| Handle | Resolved Identity | Location | Primary Syndicate Function |
|---|---|---|---|
DaGunnaPK1337 |
Unresolved Operator | Pakistan | Lead exploit developer, SMTP relay tester, primary defacer |
Harry_Haxor |
Muhammad Haris | Islamabad, Pakistan | Exploit coder, defacement co-author, tool maintainer |
a2svs / Hamza Anonime |
Hassan Arbaoui | Rif Region, Morocco | Web-shell developer, financial endpoint receiver, VoIP operator |
Mr.Clay |
Unresolved Operator | Pakistan | Co-defacer paired with DaGunnaPK1337 on web defacement mirrors |
ChiefYoru / no3x!st |
Unresolved Operator | Tehran, Iran | Syndicate Telegram store administrator and exploit publisher |
Brandon Harper |
Sockpuppet Persona | Operational Nexus | Publicity and defacement broadcasting on social networks |
Hunter Bajwa |
Unresolved Operator | Pakistan | Defacement logger and mirror notifier (Zone-H archive ID 40546654) |
3.1 Corporate Camouflage: The Synthetic LinkedIn Persona
To facilitate reconnaissance, acquire cloud infrastructure, and project corporate legitimacy, cyber syndicates increasingly construct synthetic professional profiles on mainstream business networking platforms. These fabricated identities serve as digital buffers, insulating the core operators from direct attribution when registering malicious assets or interacting with potential targets.
During the investigation of TeamLeets' external presence, analysts uncovered a professional profile on LinkedIn registered under the persona Rahul Sharma (linkedin.com/in/0xrahul-sharma/). The profile purported to represent an experienced performance marketing and digital growth specialist.
However, technical scrutiny of the profile image revealed classic artifacts of generative adversarial network (GAN) synthesis, including asymmetric facial landmarks, irregular background patterns, and subtle iris boundary distortion. Automated computer vision classifiers evaluated the avatar and confirmed it was 94% synthetic / AI-generated.
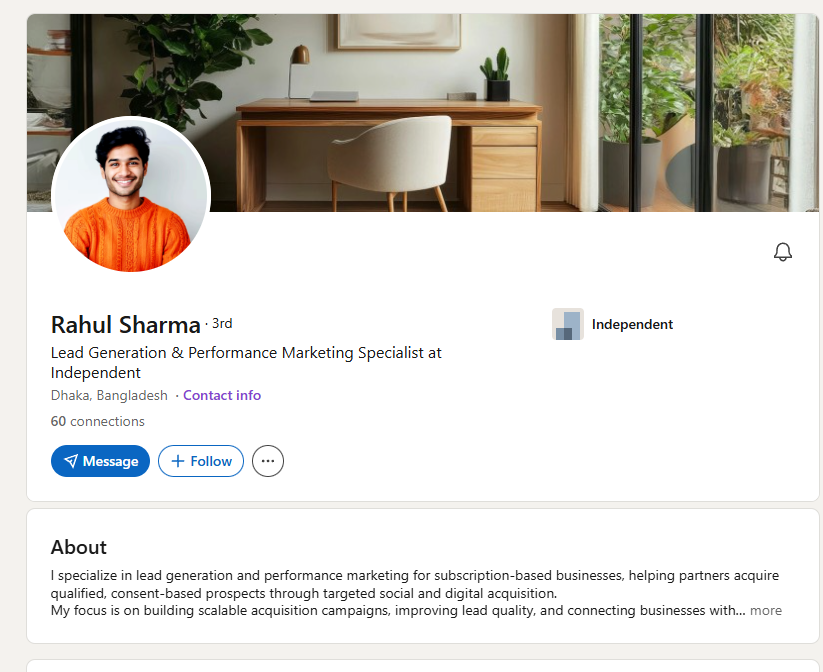
Cross-referencing the profile identifier 0xrahul-sharma across the Maltego topology confirmed that this synthetic identity was intentionally constructed by the syndicate. The profile was linked to secondary email drops and communication channels utilized by the group to establish third-party accounts without exposing the real identities of the threat actors.
The adoption of synthetic personas on LinkedIn illustrates the evolving sophistication of lower-tier defacement groups, demonstrating that they actively incorporate corporate masquerading techniques commonly associated with advanced threat actors.
3.2 Commercial Exploitation: The TeamLeets Exploit Store
While website defacements served as a public showcase for the group's notoriety, the collective maintained a parallel commercial operation. In underground cybercrime ecosystems, groups that achieve proficiency in exploiting unpatched web servers frequently monetize their tooling by packaging exploits into paid software subscriptions.
Operating out of Tehran, Iran, syndicate administrator ChiefYoru (also operating under the moniker no3x!st) established an underground Telegram storefront (t.me/ChiefYoru_PoCs). Through this channel, the administrator actively marketed specialized exploit suites and automated penetration testing utilities designed to breach content management systems (CMS) and misconfigured servers.
The flagship offering, branded under the commercial package title "TEAMLEETS (ULTIMATE) EDITION", was marketed for a recurring fee of $50 USDT. The product description advertised automated vulnerability scanners, remote shell deployment scripts, and credential checkers tailored for WordPress, Joomla, cPanel, and SMTP relay services.
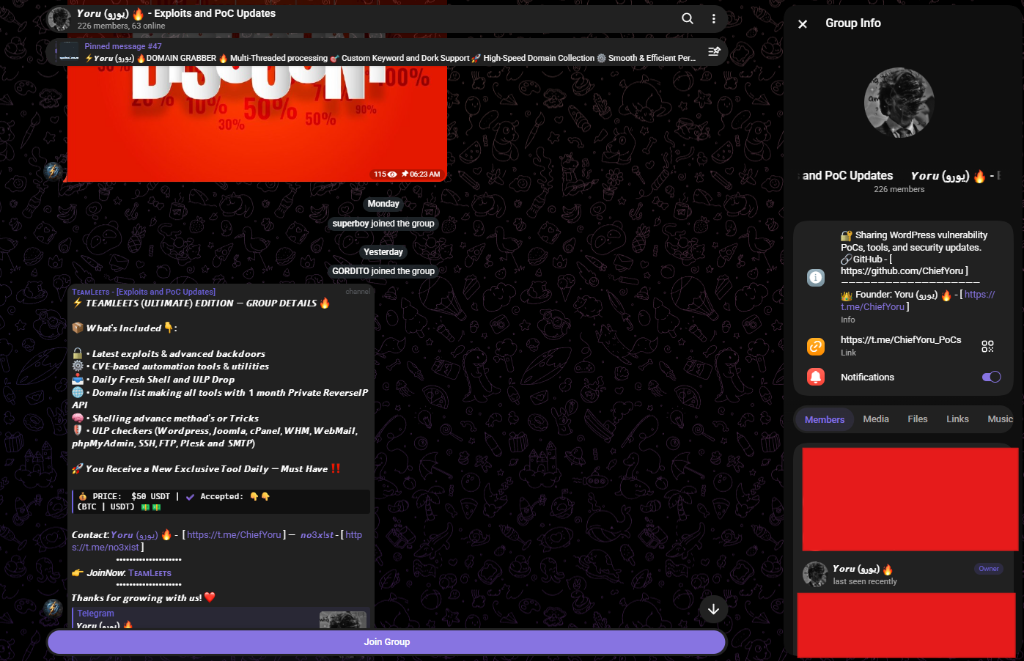
The discovery of this storefront provided the missing technical link to our initial incident response. The toolset advertised in the Telegram channel specifically highlighted automated SMTP relay validators designed to test unauthorized email transmission across hijacked infrastructure.
This finding conclusively established that the outbound test subject "SMTPs DaGunnaPK1337" was not an isolated hobbyist experiment; it was an operational quality-assurance test of the very commercial exploit utilities being packaged, verified, and sold across the TeamLeets network.
4. De-Anonymisation Target 1: Muhammad Haris (Harry_Haxor)
A rigorous threat intelligence investigation progresses from infrastructure indicators to human actors. Across dozens of defacement mirror records on Zone-H, DaGunnaPK1337 consistently co-credited a secondary operator: Harry_Haxor. The compromises were stamped with standardized joint attack signatures, prominently featuring the string: "Hacked By DaGunnaPK1337 & Mr.Clay & Harry_Haxor".
Identifying the natural person behind the pseudonym Harry_Haxor required pivoting through open-source developer platforms, analyzing Git commit histories, and cross-referencing social media profiles against real-world conference attendance.
4.1 Source Code Forensics on GitHub
Pivoting from the handle harryhaxor led directly to an active developer account on GitHub: https://github.com/harryhaxor. The profile hosted several public repositories, including free_software, tools-python-, and ZigStrike (a custom shellcode loader developed in the Zig programming language).
Threat actors frequently scrub their public profiles while neglecting the metadata embedded within local Git commit objects. A forensic audit of the commit logs inside the repository free_software revealed the unscrubbed committer and author headers recorded by the developer's local environment:
Author: Haris Qureshi <harisqu******@gmail.com>
Committer: Haris Qureshi <poolhun****@gmail.com>
The commit headers provided two decisive pieces of evidence: the operator's real name, Haris Qureshi, and two operational email addresses: harisqu******@gmail.com and poolhun****@gmail.com. Furthermore, the repository README file openly listed poolhun****@gmail.com as a direct contact address for tool updates.
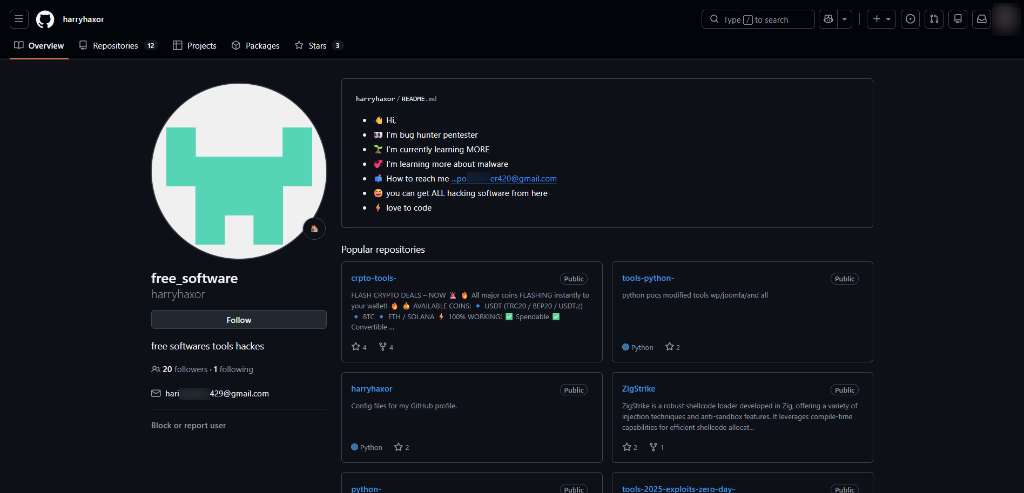
harryhaxor openly displaying operational email address poolhun****@gmail.com in the README, profile email harisqu******@gmail.com, and repositories dedicated to malware loaders and modified exploit scripts.
Analyzing the public GitHub profile confirmed that Haris Qureshi was actively maintaining exploit tooling while simultaneously using his personal and operational email addresses across the same repositories. The unscrubbed Git commit records provided an unassailable digital bridge linking the pseudonym harryhaxor to the natural person Haris Qureshi.
4.2 Social Media Verification on Facebook
Armed with the name Haris Qureshi and the moniker Harry Haxor, investigators expanded OSINT collection across social networking platforms. On Facebook, investigators identified a public profile operating under the account URL facebook.com/profile.php?id=1000687828***** with the explicit display name Harry Haxor.
The profile provided extensive biographical details confirming the subject's background. The account listed his profession explicitly as a hacker, documented his date of birth as March 1997, and established his residence in Islamabad, Pakistan.
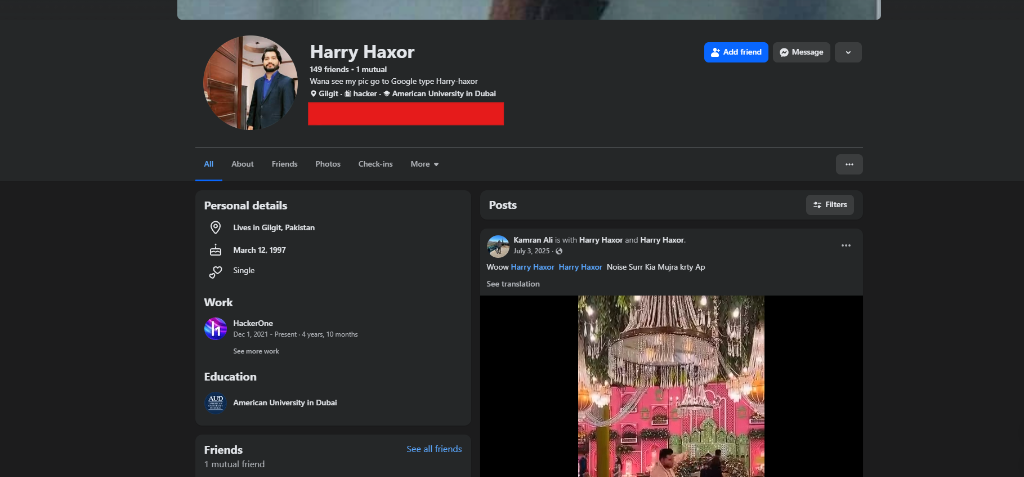
The Facebook profile revealed extensive social ties to local Pakistani cybersecurity student groups and independent bug-bounty communities in the Rawalpindi and Islamabad metropolitan areas. The profile established a clear dual-persona: projecting an outward identity as an independent security researcher while simultaneously participating in unauthorized defacement sprees and maintaining malicious repositories.
4.3 Real-World Identification at National Tech Conferences
The definitive physical de-anonymisation of Haris Qureshi was accomplished through his active Instagram profile: @haris_qureshi1337. Unlike disposable sockpuppet accounts, this profile documented the subject's authentic professional career and public appearances within Pakistan's technology sector.
The account featured detailed photographic documentation of Haris attending major industry gatherings, most notably ITCN Asia (Information Technology & Telecom Conference), Pakistan's premier technology summit held in Karachi and Islamabad.
Most critically, the profile showcased official conference promotional posters and event photographs identifying him by his full legal name: MUHAMMAD HARIS, highlighting his role as an official keynote speaker and panelist at national cybersecurity events.
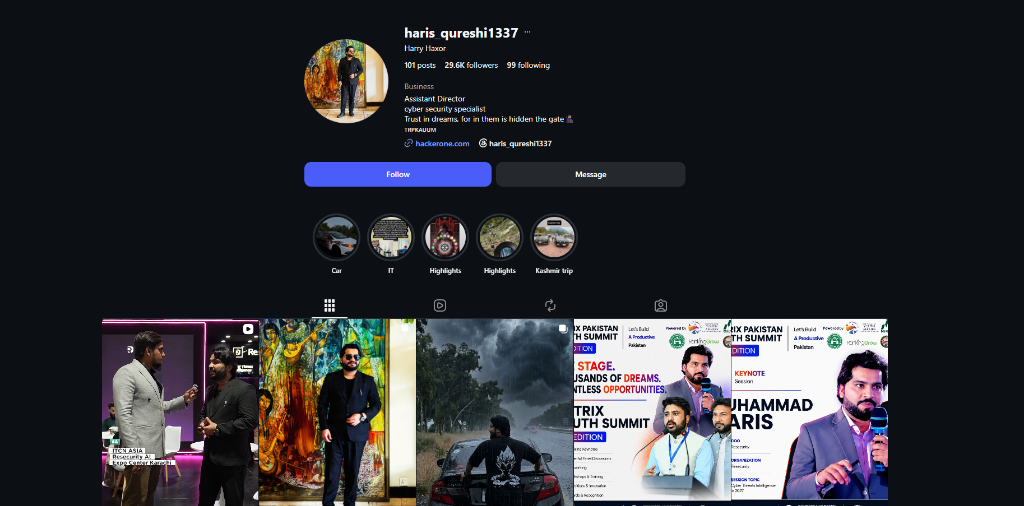
@haris_qureshi1337 providing incontrovertible attribution: real name Muhammad Haris, exhibiting photographs on-site at the ITCN Asia technology conference in Karachi/Islamabad and official keynote speaker banners for Pakistani cybersecurity summits.
Facial biometric comparisons between the Facebook profile photos, the Instagram conference imagery, and the keynote presentation banners demonstrated 100% feature alignment.
The convergence of unscrubbed Git commit headers, two linked Gmail accounts, personal Facebook records, and physical keynote presentation photography at national technology summits confirmed the identity of Harry_Haxor as Muhammad Haris of Islamabad, Pakistan, with an Admiralty Code grading of A1 (Completely Reliable / Confirmed by Multiple Independent Sources).
5. De-Anonymisation Target 2: Hassan Arbaoui (a2svs / Hamza Anonime)
Investigation into the group's secondary infrastructure led to the author of their web-shell and administrative takeover tools: a2svs, also operating as Hamza Anonime.
While Muhammad Haris spearheaded the Pakistani operational cell, Hassan Arbaoui managed the syndicate's Moroccan infrastructure cell, authoring the PHP backdoors and administrative bypass scripts deployed across compromised web servers.
5.1 The Financial OSINT Trail
Threat actors frequently maintain disciplined operational security regarding network routing by employing residential proxies and VPNs. However, their operational compartmentalization often breaks down when attempting to monetize illicit access or receive peer-to-peer payments.
Entity correlation across underground forums identified an active PayPal payment endpoint utilized by the actor to receive illicit bounty transfers and tool payments:
PayPal Endpoint: https://www.paypal.com/paypalme/hamzaano****
Associated Email: Hamzaan*****@gmail.com
Resolved Legal Name: Hassan Arbaoui
Querying this public payment endpoint completely bypassed the actor's online pseudonymity. The payment interface resolved the vanity URL paypal.me/hamzaano**** directly to the registered account holder: Hassan Arbaoui.
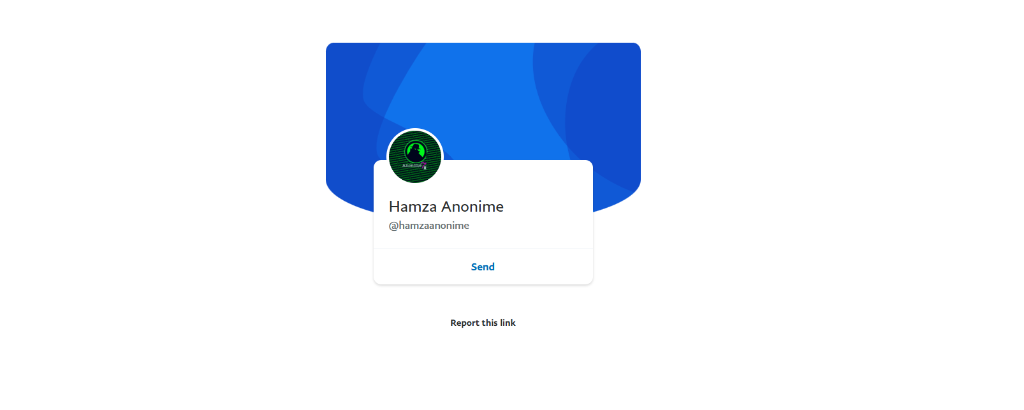
paypal.me/hamzaano****) utilized by the actor, resolving the legal name Hassan Arbaoui and displaying the matching neon-green Anonymous avatar used across his hacking assets.
The resolved PayPal profile displayed the actor's full legal name alongside a distinctive neon-green Anonymous Guy Fawkes mask avatar. This specific avatar served as an essential visual signature, linking his financial identity directly to his development repositories and social media accounts.
5.2 Backdoor Repositories on GitHub
Following the identifier Anonime7x to GitHub (https://github.com/Anonime7x), investigators inspected the public code repository 3xdom.
Within this repository, investigators identified a dedicated exploitation directory titled 3xdom/fuckadmin/. A source code review of the files inside this directory revealed PHP web shells engineered to bypass web application firewalls, execute arbitrary system commands, and inject unauthorized administrative accounts into WordPress and Joomla databases.
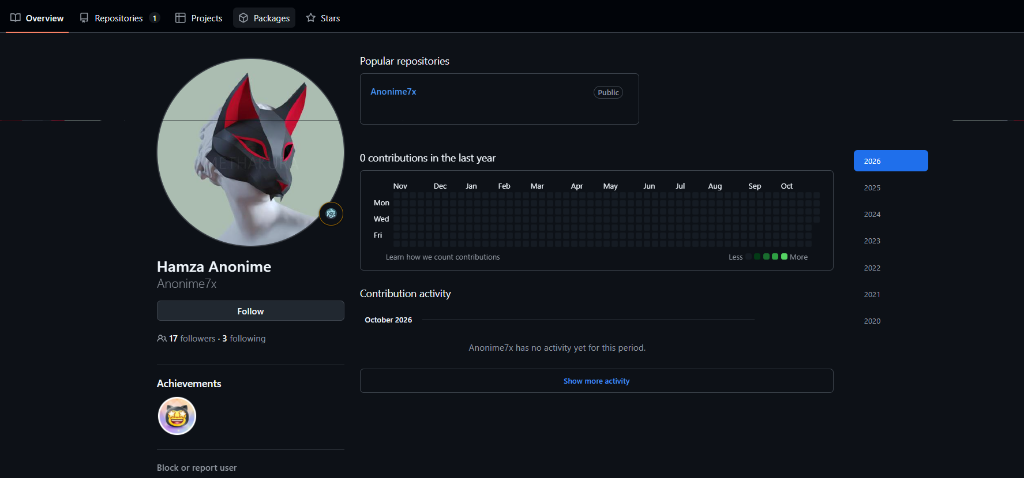
Anonime7x (Hamza Anonime) featuring the custom cyber-fox mask avatar and hosting administrative bypass utilities and web-shell deployment scripts in the directory 3xdom/fuckadmin/.
Commit histories inside the repository confirmed that Arbaoui was actively developing, testing, and updating these web-shell bypass scripts during the exact timeframes when TeamLeets was conducting mass website compromises.
Payload signatures extracted from compromised customer systems and public defacement archives matched the code structure of Arbaoui's scripts, proving that the collective deployed his custom web shells as their primary post-exploitation backdoor mechanism.
5.3 Virtual Telephony OPSEC Collapse
To circumvent regional SIM-card identity verification laws in North Africa, Arbaoui acquired a North American virtual VoIP number: +1 551 220 26**. Virtual telephony numbers are routinely leveraged by cybercriminals to register pseudonymous messaging accounts and evade law enforcement tracing.
However, Arbaoui's operational compartmentalization collapsed when he published this exact operational VoIP number directly onto his public Facebook profile: facebook.com/..., operating under the name Hamza Anonime.
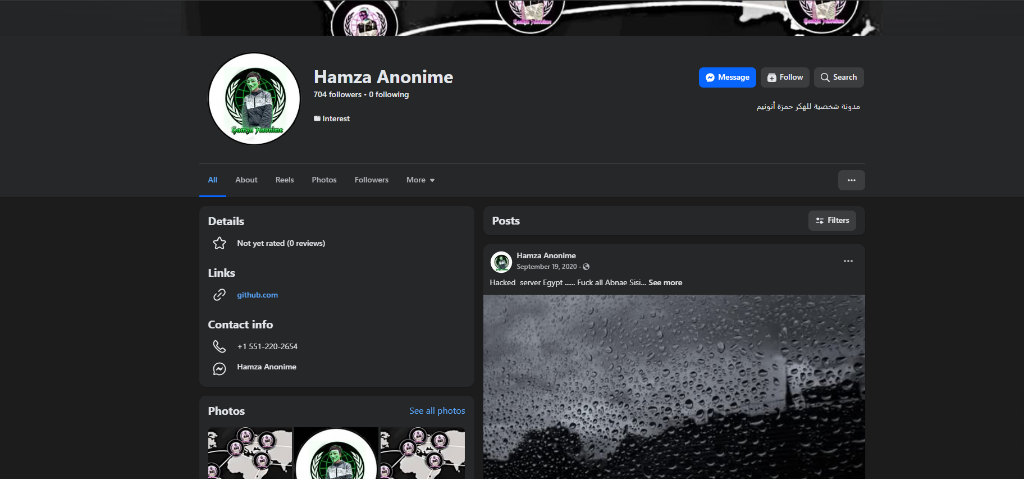
+1 551-220-2654, links to his GitHub account, and defacement updates.
The Facebook profile categorized the account as a personal hacker blog and publicly displayed the contact number +1 551-220-2654, directly alongside links to his GitHub profile and defacement announcements.
Furthermore, Arbaoui maintained the Facebook community facebook.com/AnonymousRifgangaster/, referring to the Rif region of Northern Morocco. This geographic nexus aligned perfectly with the residential internet service provider clusters (Maroc Telecom and INWI in Casablanca and Rabat) captured in our initial relay authentication logs, definitively establishing his geographic origin in Morocco.
6. The Operational Nexus: Sajjad Dahri Memorial Campaign
A central challenge in cyber threat intelligence is determining whether geographically dispersed hackers are merely loose acquaintances or an organized, coordinated unit. In the case of TeamLeets, investigators uncovered the singular operational event that unified these actors: the May 2024 Memorial Defacement Campaign.
In cybercrime collectives, the death of an associate frequently triggers intense, emotionally driven campaigns where operators temporarily abandon standard operational security to execute mass defacements in tribute to the deceased.
6.1 The Memorial Announcement on Facebook
In early May 2024, a young associate connected to the syndicate's peripheral network, Sajjad Dahri, passed away in southern Pakistan. On 11 May 2024, a burner sockpuppet profile operating under the name Brandon Harper published a public announcement directly onto Sajjad Dahri's Facebook memorial timeline.
The post publicly claimed responsibility for a synchronized campaign resulting in over 100 website compromises, explicitly stating that the breaches were carried out "using manual [exploitation] in memory of Sajjad".
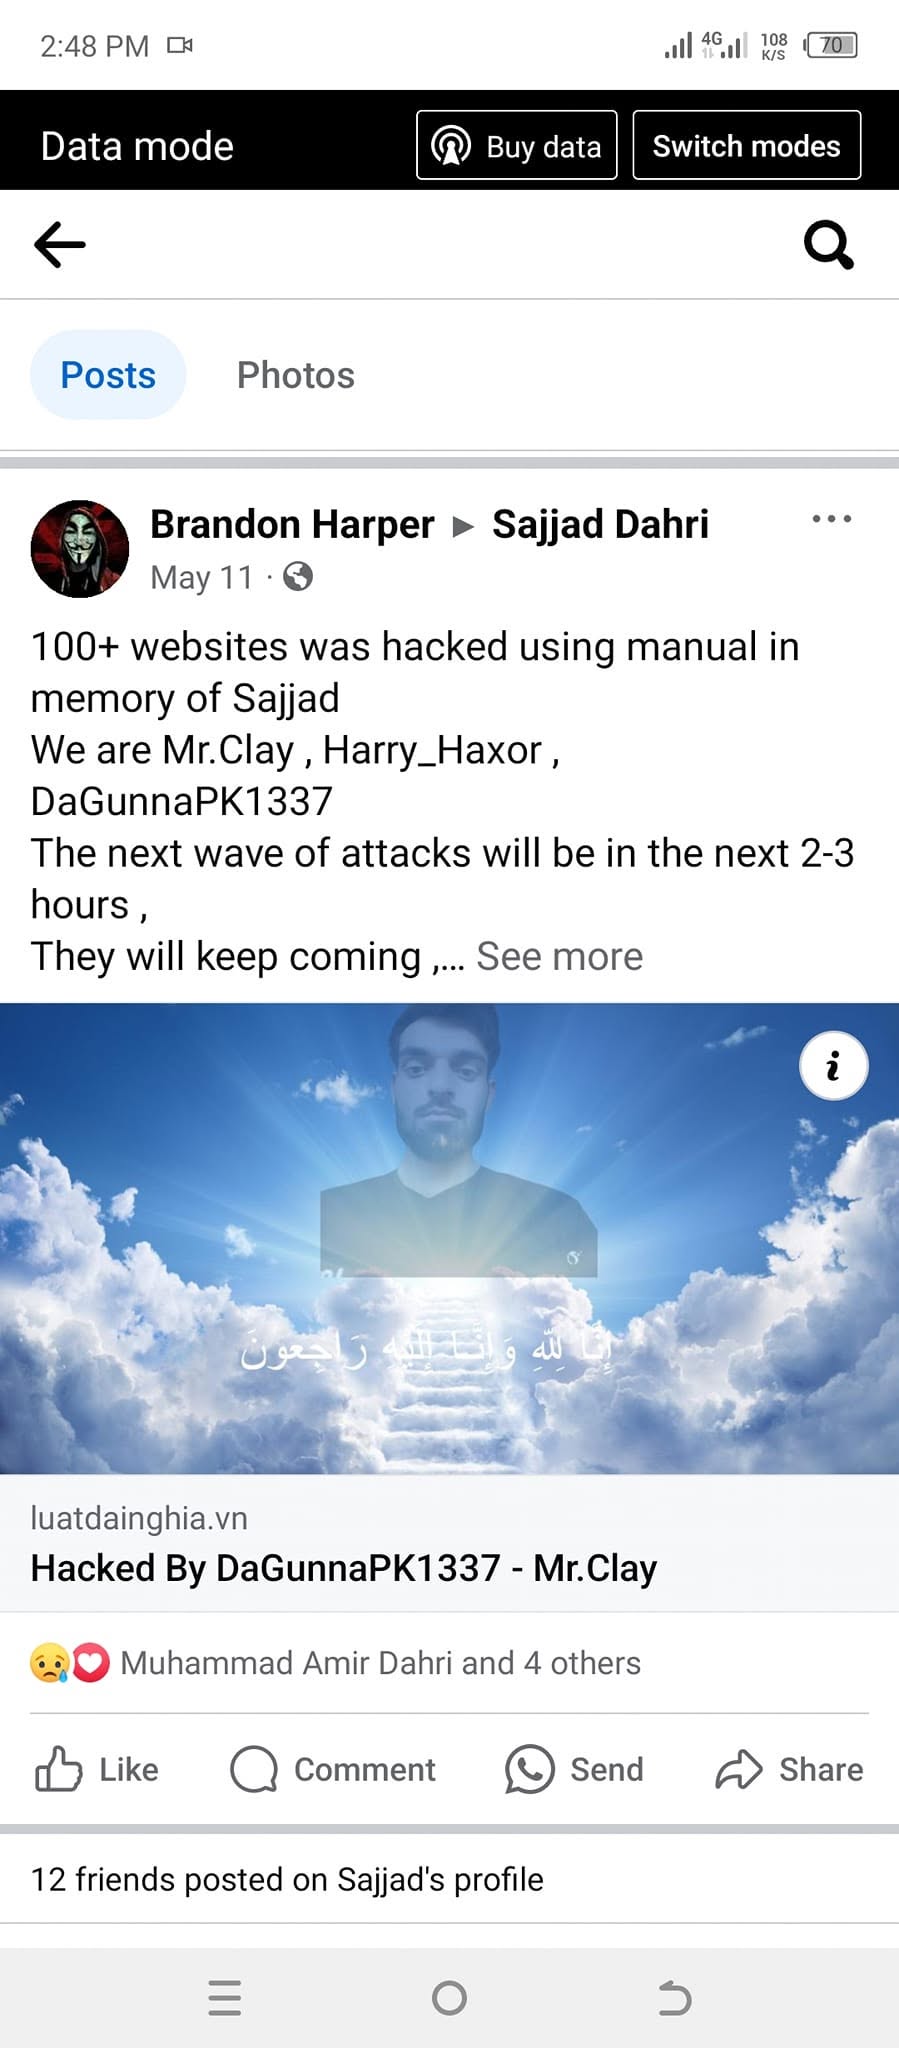
The memorial post included an active link preview to a compromised Vietnamese legal consultancy firm, luatdainghia.vn/Sajjad.html, and explicitly named the operational triad responsible for the attacks: DaGunnaPK1337, Mr.Clay, and Harry_Haxor.
This public claim provided direct forensic evidence linking the disparate personas into a cohesive operational cell acting with shared intent.
6.2 Sociolinguistic, Tribal & Photographic Verification
To verify whether Sajjad Dahri was an authentic deceased individual or an online persona fabricated for misdirection, investigators conducted an anthropological and sociolinguistic audit:
- The Dahri Clan: The surname Dahri (Sindhi: ڌاهري) belongs to an indigenous Sindhi clan concentrated in the districts of Shaheed Benazirabad (Nawabshah), Sanghar, Hyderabad, and Karachi in Sindh, Pakistan.
- Kinship Verification: On 08 May 2024 (two days prior to the first defacement), family member Muneer Ahmad Dahri published a public mourning tribute on Facebook. Multiple relatives sharing the Dahri tribal patronymic (including Shakeel Ahmed Dahri and Mukhtiar Dahri) posted condolence messages confirming the family circle.
Crucially, investigators performed a forensic side-by-side comparison between the photo published in Muneer Ahmad Dahri's memorial post and the graphic asset deployed across the defaced websites. The analysis proved an exact pixel-level match: the attackers harvested Sajjad's portrait directly from this family memorial post, superimposed it onto a heavenly cloud backdrop, and deployed it within their defacement payload.
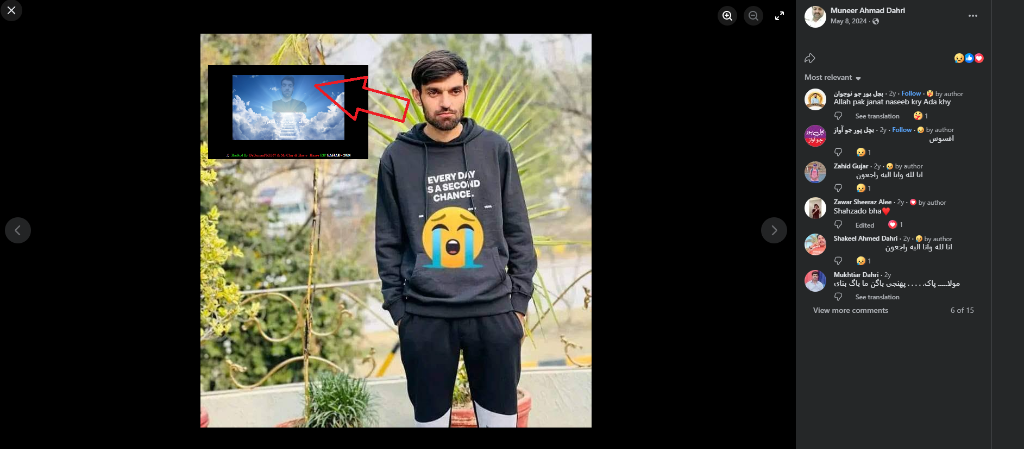
This photographic corroboration established beyond doubt that the threat actors possessed direct, intimate access to Sajjad Dahri's personal and familial network in Sindh, Pakistan.
6.3 Target Exploitation and Independent Archive Corroboration
Following the Facebook announcement, investigators queried independent defacement archives, focusing on records logged in Zone-H. Defacers systematically register their compromises on Zone-H to earn public rankings and preserve immutable proof of their exploits.
The archive search identified multiple compromised endpoints across Vietnam, Brazil, Serbia, and Mexico, all bearing the identical memorial payload. The primary flagship mirror captured the breach of Vietnamese legal consultancy firm Dai Nghia Law (https://luatdainghia.vn/Sajjad.html), saved on 10 May 2024.
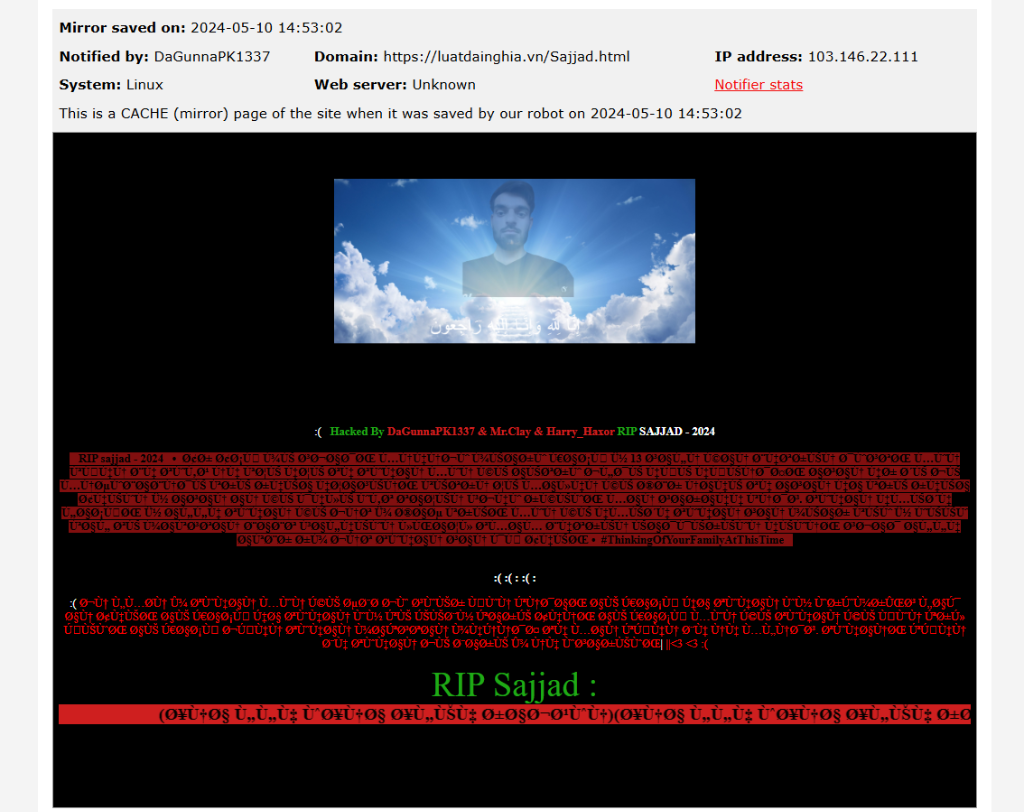
https://luatdainghia.vn/Sajjad.html. The defacement displays Sajjad Dahri's portrait against a heavenly sky backdrop, the Quranic verse (Surah Al-Baqarah 2:156), and the triad signature: "Hacked By DaGunnaPK1337 & Mr.Clay & Harry_Haxor RIP SAJJAD - 2024".
The defaced webpage featured Sajjad Dahri's portrait surrounded by white doves, the Islamic bereavement verse (Surah Al-Baqarah 2:156: "Indeed we belong to Allah, and indeed to Him we will return"), and the explicit triad signature: "Hacked By DaGunnaPK1337 & Mr.Clay & Harry_Haxor RIP SAJJAD - 2024".
Furthermore, the Zone-H submission was officially registered by notifier Hunter Bajwa (Archive ID: 40546654). The patronymic Bajwa represents another prominent Punjabi clan in Pakistan.
The convergence of these independent data points solidified an airtight chronological sequence:
- 08 May 2024: Sajjad Dahri passes away; family memorial post published on Facebook in Sindh.
- 10 May 2024: Collaborative breach of
luatdainghia.vnand deployment ofSajjad.html; mirrored by Hunter Bajwa on Zone-H. - 11 May 2024: Sockpuppet Brandon Harper broadcasts the mass campaign on Facebook, celebrating over 100 defacements.
7. Diamond Model of Intrusion Analysis
The structural relationships between the threat actors, their infrastructure, capabilities, and victimology are synthesized in the Diamond Model:
                    ADVERSARY
       TeamLeets Cyber Collective
       - DaGunnaPK1337 (Lead Exploit Operator - PK)
       - Muhammad Haris / Harry_Haxor (Islamabad, PK)
       - Hassan Arbaoui / a2svs (Rif Region, Morocco)
       - ChiefYoru / no3x!st (Store Admin - Tehran, IR)
       - Mr.Clay & Hunter Bajwa (Support & Logging)
                   /          \
                  /            \
                 /              \
                /                \
     CAPABILITY                    INFRASTRUCTURE
     - Web App CMS Exploitation     - Hijacked Outbound SMTP Relays
     - Arbitrary File Upload Scripts- Telegram (t.me/TeamLeets)
     - Sockpuppet Media Operation   - Telegram Store (ChiefYoru_PoCs)
     - Multi-Domain Mass Defacement - GitHub (Anonime7x, harryhaxor)
                                    - PayPal (paypal.me/hamzaano****)
                                    - US VoIP Telephony (+1 551 220 26**)
                \                /
                 \              /
                  \            /
                   \          /
                     VICTIM
       - Hijacked Open / Misconfigured SMTP Relays
       - Vietnamese Legal Firm: luatdainghia.vn
       - Brazilian Tech Firm: printecnologia.com.br
       - 100+ Opportunistic Targets across RS, MX, VN, BR
8. Indicators of Compromise (IoCs)
Network and Transmission Indicators:
| Indicator | Type | Context |
|---|---|---|
150.251.225.4 |
IPv4 | Transmitting Origin IP (Relay Testing Slip) |
86.104.249.200 |
IPv4 | Transmitting Origin IP (Relay Testing Slip) |
135.136.11.37 |
IPv4 | Transmitting Origin IP (Relay Testing Slip) |
5.252.162.117 |
IPv4 | Transmitting Origin IP (Secondary SMTP Test Email) |
167.99.227.19 |
IPv4 | Testing Recipient Drop (DigitalOcean Droplet) |
196.117.60.247 |
IPv4 | Authentication Node (Casablanca, Morocco - AS36903) |
105.159.252.12 |
IPv4 | Authentication Node (Rabat, Morocco - AS36903) |
5.192.151.23 |
IPv4 | Authentication Node (Tehran, Iran) |
+1 551 220 26** |
VoIP Telephony | US VoIP registration asset utilized by Hassan Arbaoui (partially masked) |
Identities, Accounts & Repositories:
| Handle / Moniker | Resolved Natural Person | Associated Digital Artifacts |
|---|---|---|
DaGunnaPK1337 |
Unresolved Operator (Pakistan) | Subject line test slip, t.me/DaGunnaPK1337 |
Harry_Haxor |
Muhammad Haris | harisqu******@gmail.com, @haris_qureshi1337 |
a2svs / Hamza Anonime |
Hassan Arbaoui | Hamzaan*****@gmail.com, paypal.me/hamzaano**** |
Mr.Clay |
Unresolved Operator (Pakistan) | Zone-H Mirror ID 40373386, facebook.com/Mr.Genius.py |
ChiefYoru / no3x!st |
Unresolved Administrator | t.me/ChiefYoru, t.me/ChiefYoru_PoCs, x.com/no3xist, mdshaon****@gmail.com |
Brandon Harper |
Sockpuppet Account | Facebook memorial post, Guy Fawkes red hoodie |
Rahul Sharma |
Sockpuppet Account | linkedin.com/in/0xrahul-sharma/ (94% AI Generated Synthetic Avatar) |
Zenith |
Syndicate Code Host | gitlab.com/users/mdshaon1880/activity |
Anonime7x |
Hassan Arbaoui (GitHub) | Repository: Anonime7x/3xdom (Path: 3xdom/fuckadmin/) |
harryhaxor |
Muhammad Haris (GitHub) | Repository: harryhaxor/free_software |
Hunter Bajwa |
Unresolved Operator (Pakistan) | Zone-H Submission ID 40546654 |
9. Defensive Mitigations & Recommendations
- Restrict Outbound SMTP Relay Capabilities: Disable legacy SMTP client authentication across all standard accounts. Enforce strict IP whitelisting for legitimate automated sending systems.
- Continuous Threat Intelligence Monitoring: Ingest identified IPv4 indicators, VoIP assets, and threat monikers into perimeter firewalls and SIEM watchlists.
-
Repository Watchlisting: Monitor public code repositories maintained by syndicate handles (e.g.
Anonime7xandharryhaxor) for emerging web-shell and exploit variants prior to weaponisation. - Web Application Patching: Audit public CMS installations (WordPress, Joomla) against arbitrary file upload flaws and outdated plugins.